Connect Oracle Cloud Infrastructure (OCI) for user access review (roster, MFA, offboarding) plus compute, storage, database, and network posture monitoring.
LowerPlane connects to Oracle Cloud Infrastructure using an API signing key with read-only policies: you create a dedicated OCI user, generate an API key pair, and provide LowerPlane the private key, which is stored encrypted at rest. This provides visibility into your OCI security posture across compute, storage, networking, and database services.
Flow log configuration per subnet (not log contents)
LowerPlane reads resources from your tenancy’s home region only — the region you enter when connecting. Compute, storage, databases, and networks in other subscribed regions are not scanned.
| Load Balancer | Load balancer health, connection monitoring |
| IAM | Users, groups, policies |
| Monitoring | Alarm definitions for CPU, storage, and connections |
Beyond infrastructure posture, LowerPlane reviews who has access to your OCI tenancy — the IAM user roster, admin roles, MFA enrollment, and offboarding status.
Users are matched to a person in your HR directory by email, and admin status is derived from membership of the Administrators group. For MFA, LowerPlane prefers each Identity Domain’s own per-user enrollment status and falls back to the classic isMfaActivated flag when the domain cannot be read — see the optional domain role in the setup steps below.
MFA enabled
Flags any OCI IAM user who does not have multi-factor authentication activated.
Offboarded access removed
Flags OCI access still active for an employee offboarded in your HR directory.
User identified
Confirms each IAM account resolves to a named person, not an anonymous or shared account.
Access valid
Verifies each account maps to a current employee in your HR directory whose access has been reviewed.
LowerPlane connects with an OCI API signing key: you create a read-only OCI user, generate an API key pair, and give LowerPlane the private key — which LowerPlane stores encrypted at rest.
1
Copy your tenancy OCID and home region
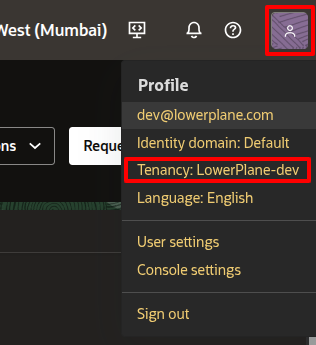
Sign in to the OCI Console, open the profile menu (top-right), and select your tenancy.
Open the profile menu and select your tenancy.
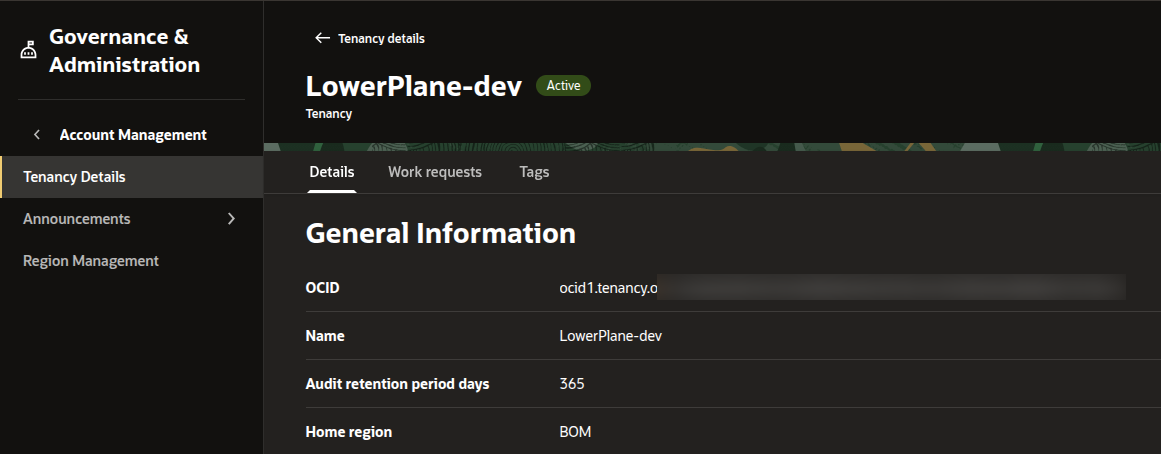
On Tenancy details, copy the OCID and note the Home region.
Tenancy details shows the tenancy OCID and the home region.
Use the region identifier, not the region code. Tenancy details shows the home region as a short code (for example BOM for Mumbai), but LowerPlane needs the region identifier — ap-mumbai-1. Common mappings: BOM → ap-mumbai-1, IAD → us-ashburn-1, PHX → us-phoenix-1, FRA → eu-frankfurt-1, LHR → uk-london-1. See Oracle’s Regions and Availability Domains for the full list.
2
Open your identity domain and create the auditor group
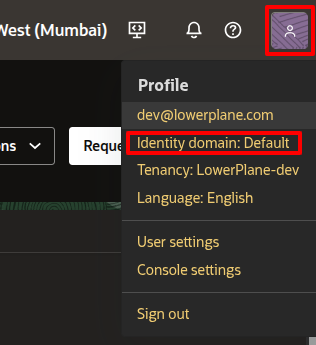
In the profile menu, note your identity domain (e.g. Default) and open it.
Your identity domain (e.g. Default) is shown in the profile menu.
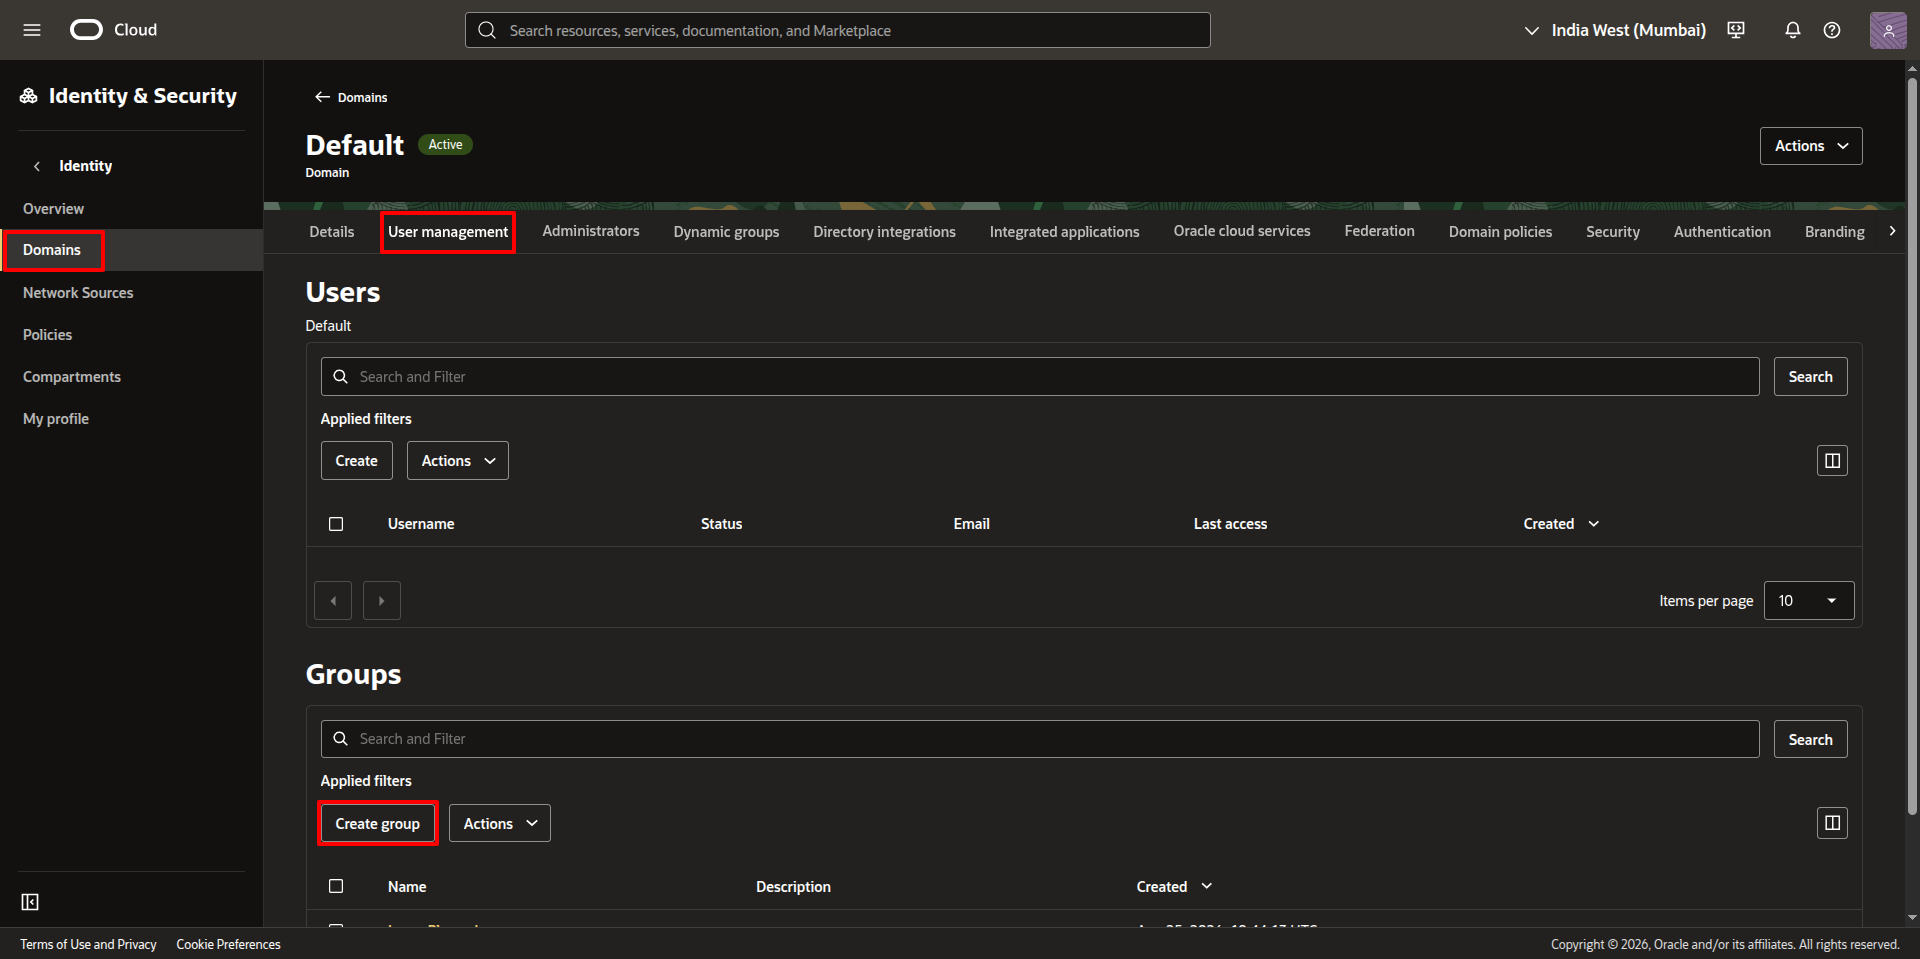
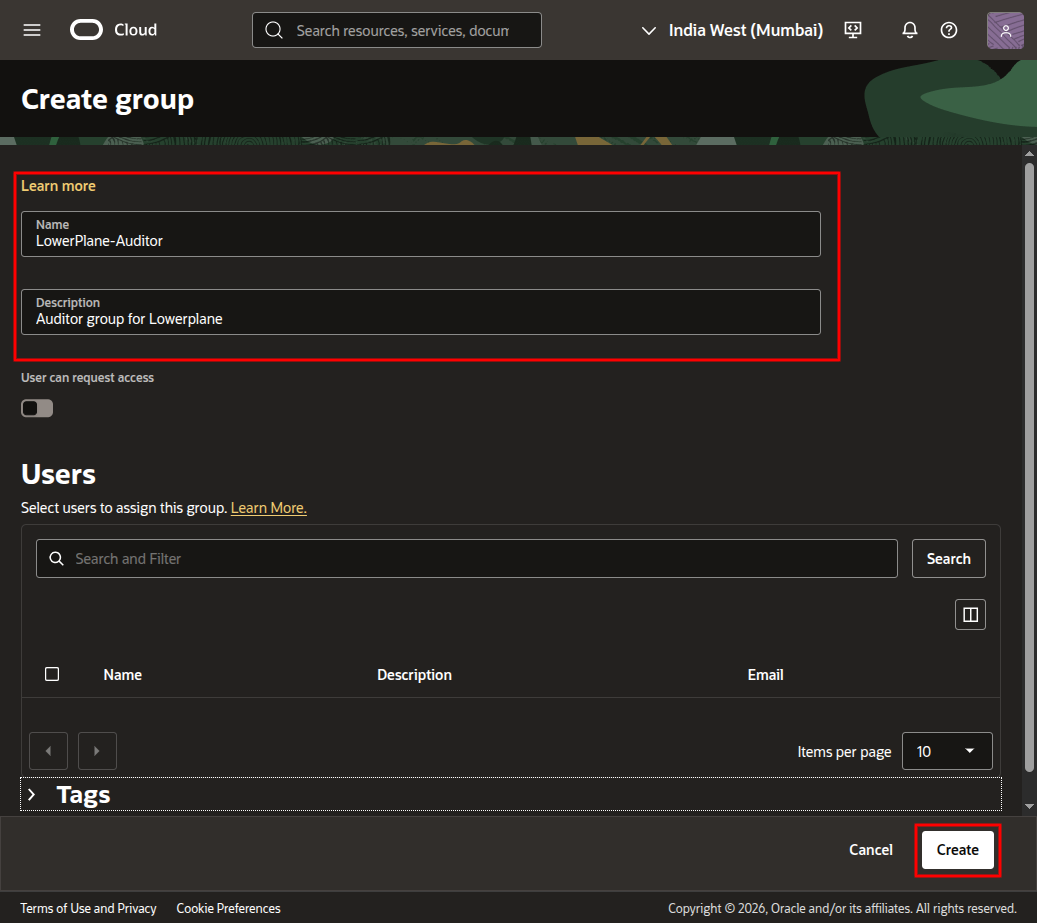
Go to Identity & Security → Domains → your domain → User management. Under Groups, click Create group and name it LowerPlane-Auditor.
Identity → Domains → your domain → User management → Groups → Create group.
Name the group LowerPlane-Auditor and click Create.
3
Create a service user and copy its OCID
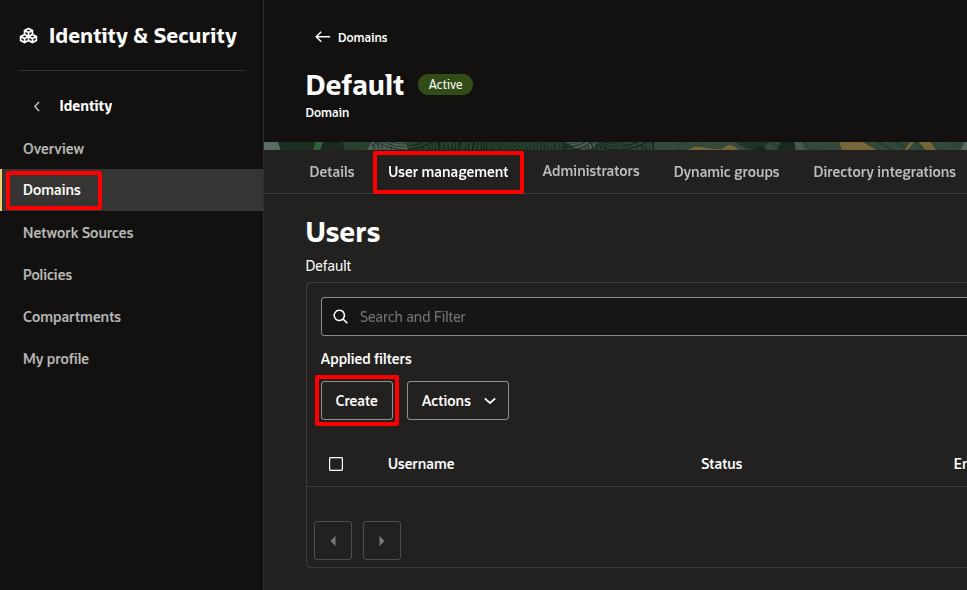
Under User management → Users, click Create.
User management → Users → Create.
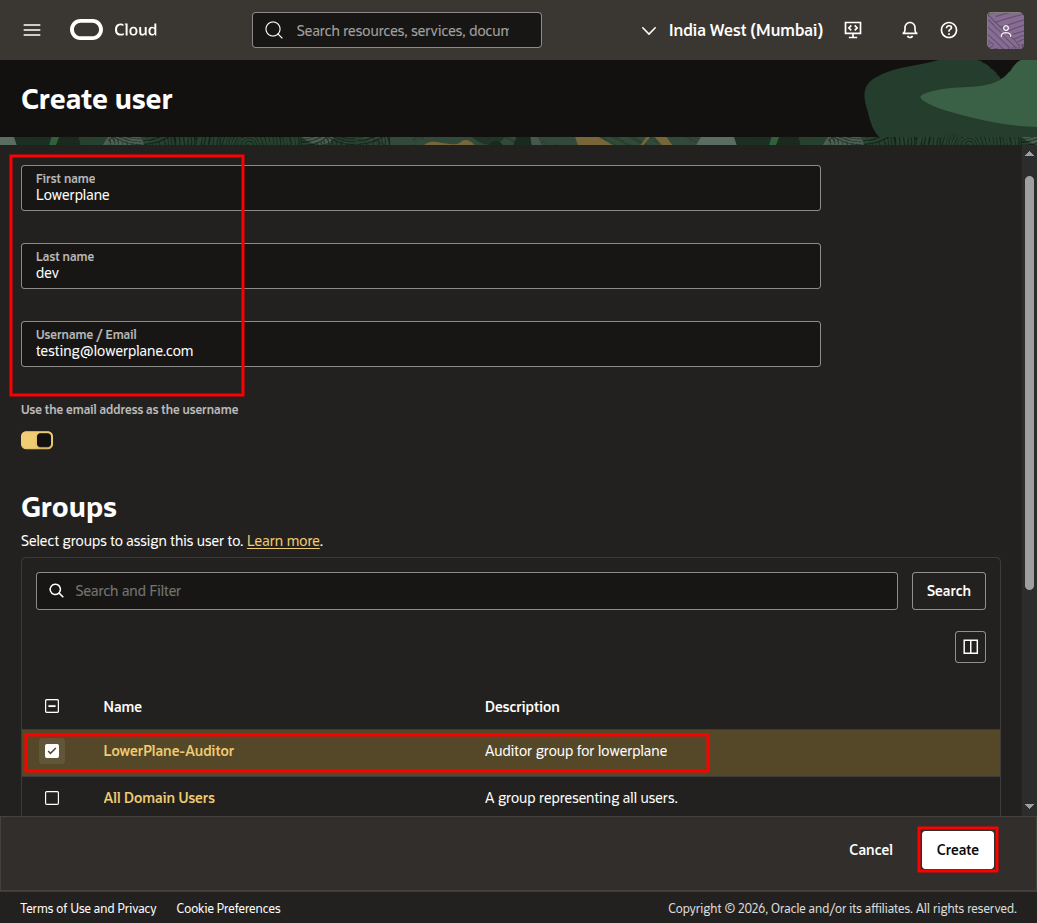
Enter a name and email for a dedicated service user, assign it to the LowerPlane-Auditor group, and click Create.
Create the service user and add it to the LowerPlane-Auditor group.
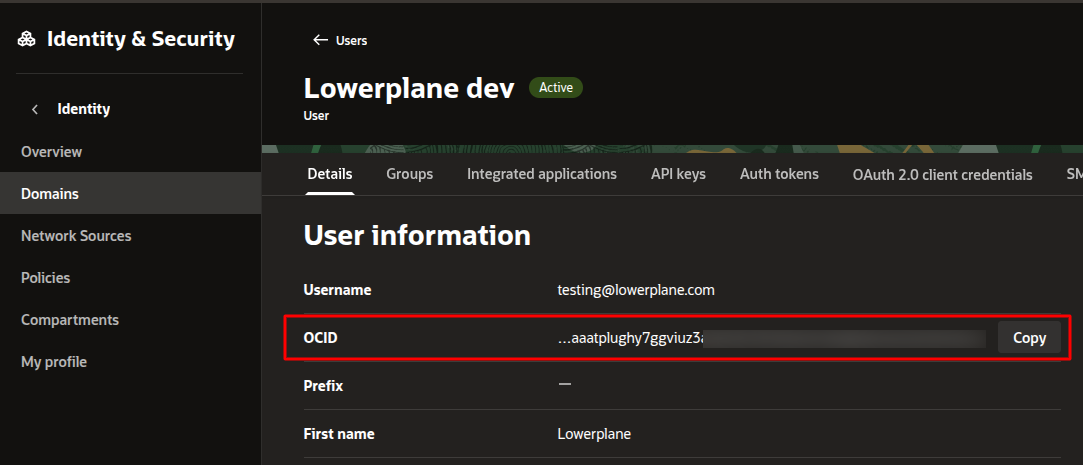
Open the new user and copy its OCID from the Details tab.
Copy the service user's OCID from its Details tab.
4
Generate an API signing key and copy the fingerprint
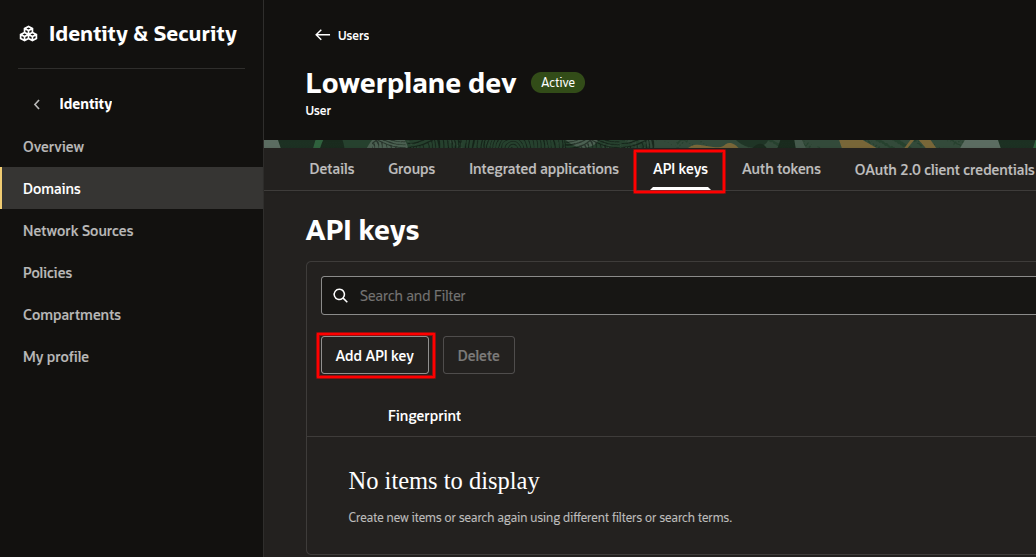
On the service user, open the API keys tab and click Add API key.
User → API keys → Add API key.
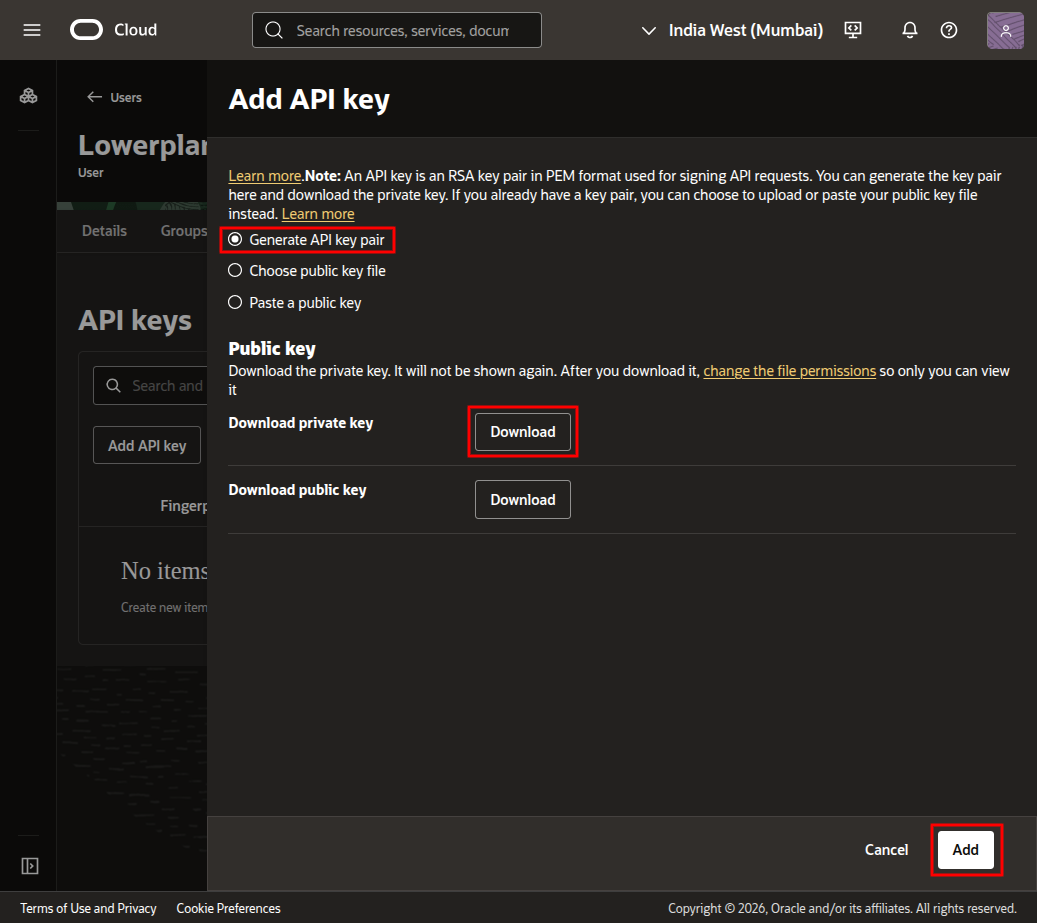
Choose Generate API key pair, click Download to save the private key (it is shown only once), then click Add. You paste this private key into LowerPlane, which stores it encrypted at rest.
Generate the key pair, download the private key, then click Add.
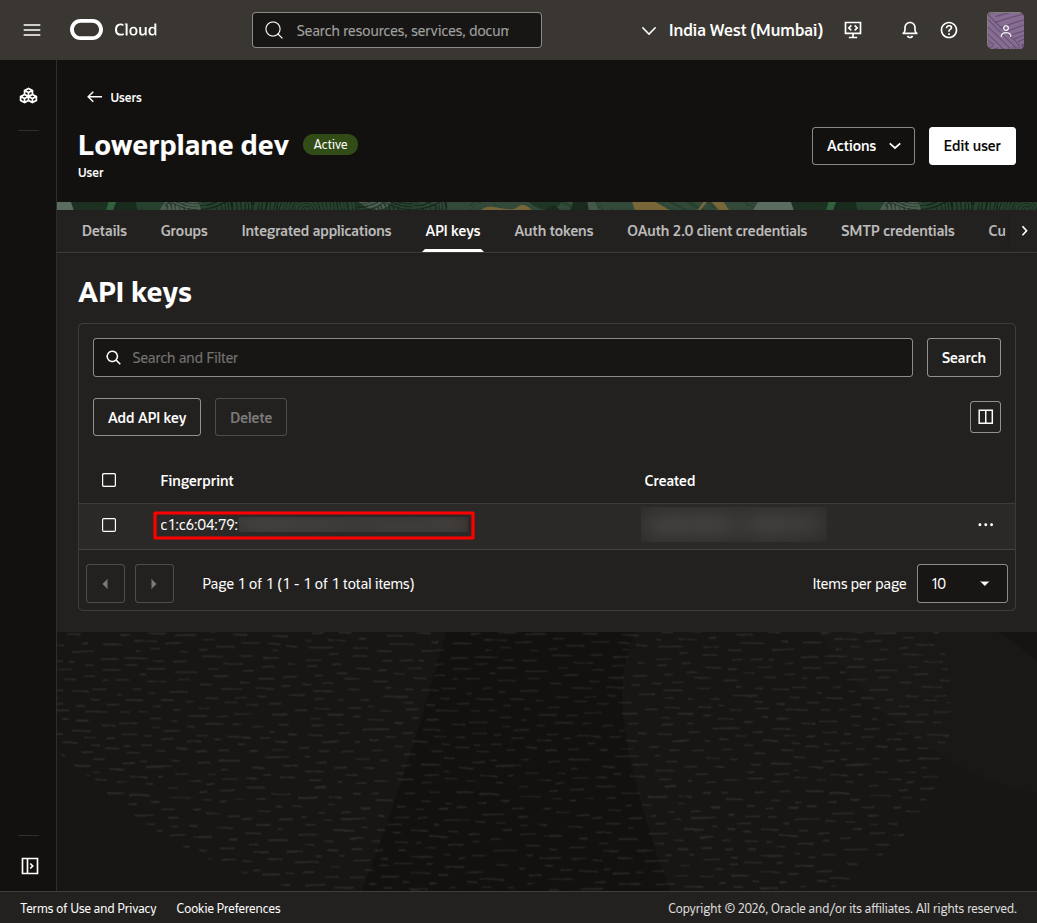
Copy the Fingerprint shown for the new key.
Copy the fingerprint of the key you just added.
5
Create the read-only policy
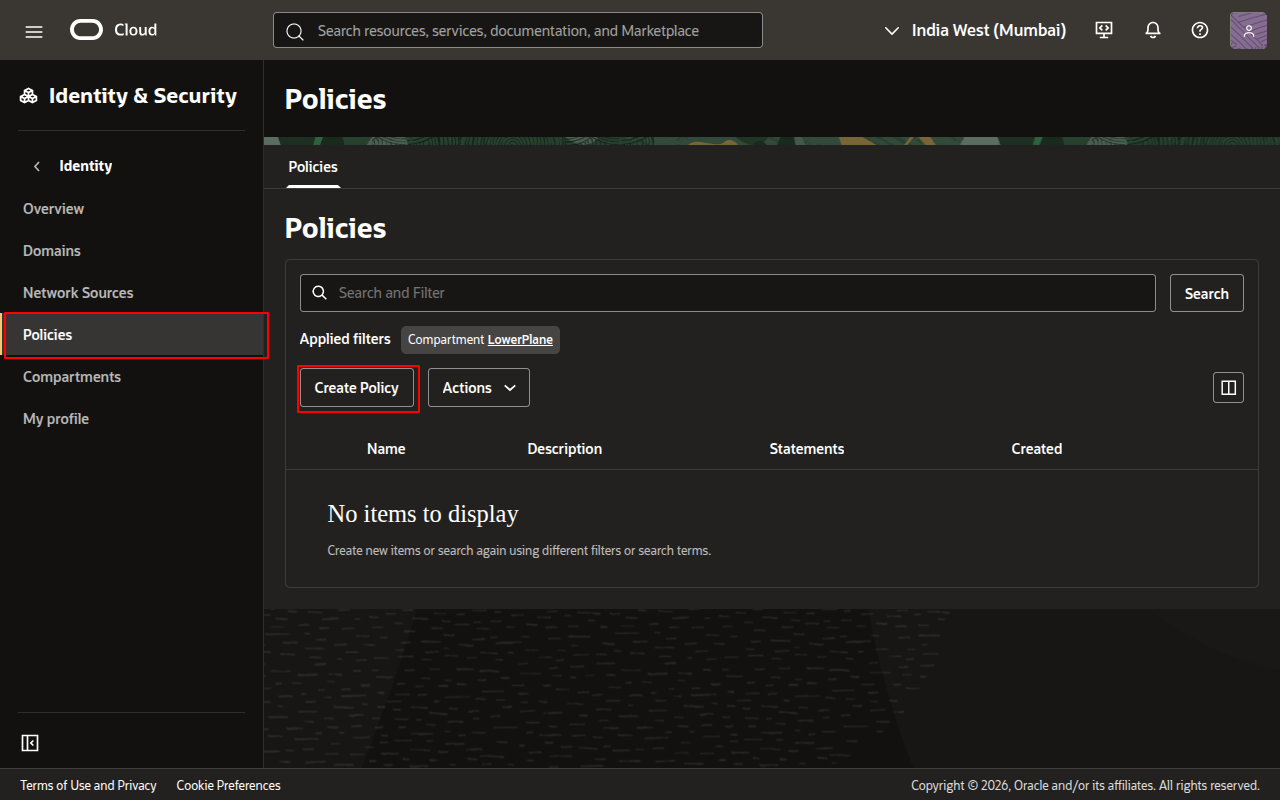
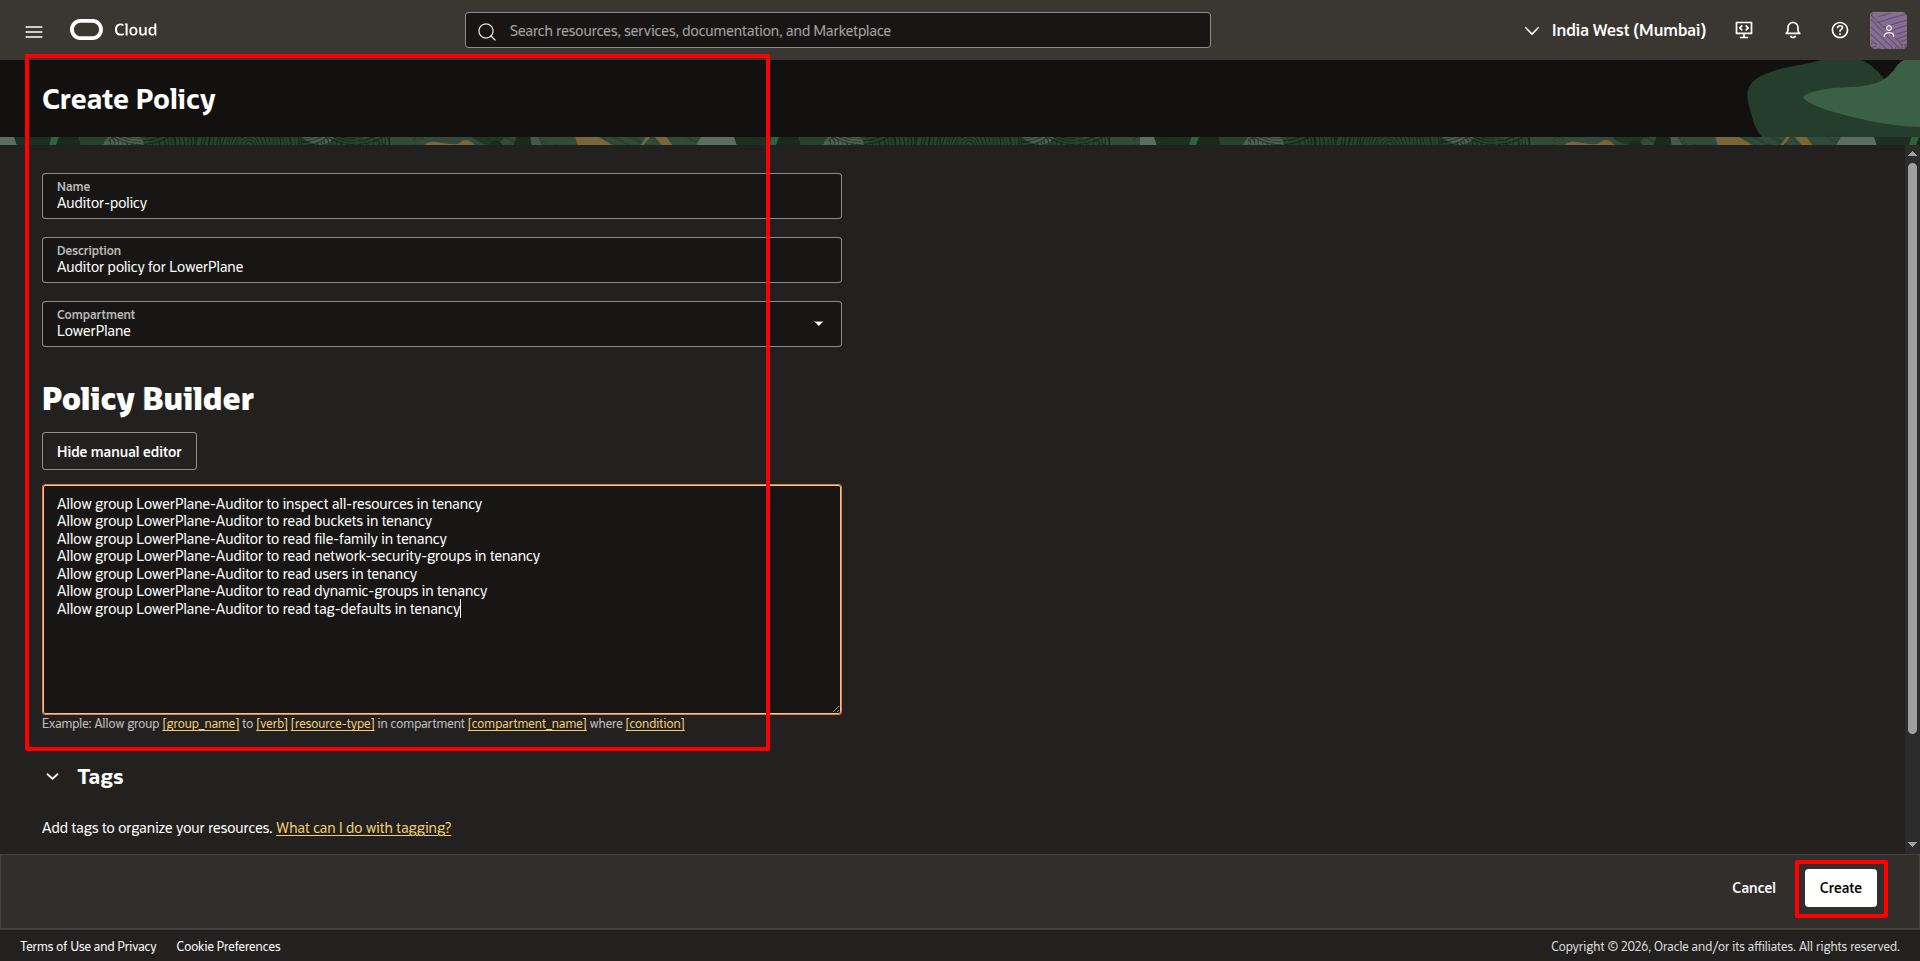
Open Identity & Security → Policies and click Create Policy.
Identity → Policies → Create Policy.
Name it Auditor-Policy, scope it to the root compartment, switch the Policy Builder to Show manual editor, and paste these seven statements:
Allow group LowerPlane-Auditor to inspect all-resources in tenancyAllow group LowerPlane-Auditor to read buckets in tenancyAllow group LowerPlane-Auditor to read file-family in tenancyAllow group LowerPlane-Auditor to read network-security-groups in tenancyAllow group LowerPlane-Auditor to read users in tenancyAllow group LowerPlane-Auditor to read dynamic-groups in tenancyAllow group LowerPlane-Auditor to read tag-defaults in tenancy
The first statement lets LowerPlane list the resources across your tenancy — compute, databases, networking, load balancers, monitoring alarms, vaults, and logs. The other six give it the full details of buckets, file systems, network security groups, users, dynamic groups, and tag defaults. inspect and read are both read-only: neither can change anything.
LowerPlane only issues GET requests. It cannot create, update, or delete any resource in your tenancy.
Paste the seven statements into the manual Policy Builder, then click Create.
Optional: MFA enrollment for Identity Domains tenancies
If your tenancy uses Identity Domains, per-user MFA enrollment lives in the domain’s own SCIM API rather than in classic IAM. Reading it needs an Identity Domain read role on the LowerPlane-Auditor group, granted inside the domain under Domains → your domain → Groups → LowerPlane-Auditor → Roles.This is optional. Without it LowerPlane falls back to the classic isMfaActivated flag, and every other check is unaffected.
6
Connect in LowerPlane
Go to Settings → Integrations in LowerPlane, find Oracle Cloud, click Connect, and enter:
Value
From
Tenancy OCID
Step 1 — Tenancy details
Home region
Step 1 — the region identifier, e.g. ap-mumbai-1
User OCID
Step 3 — service user Details
Fingerprint
Step 4 — the API key you added
Private key
Step 4 — the file you downloaded (stored encrypted at rest)
Compartment OCID
Optional — Identity → Compartments; leave blank to use the tenancy root
All compute instances with public IP exposure, security list restrictions, and CPU monitoring alarm status.
Object Storage
Storage buckets with encryption at rest verification (Oracle-managed or customer-managed keys).
Autonomous Databases
ATP/ADW instances with backup status, public endpoint exposure, access control lists, and monitoring alarms.
VCN & Networking
Virtual Cloud Networks, subnets, security list rules, and which subnets have an enabled flow log in the OCI Logging service.
Block Volumes
Block volumes and their encryption key type. OCI encrypts every volume at rest; LowerPlane records whether the key is Oracle-managed or a customer-managed Vault key.
Vaults
Key management vaults, their type, and lifecycle state — evidence that encryption keys are held in a dedicated service.
Load Balancers
Load balancer health and active connection monitoring alarm status.
Monitoring Alarms
OCI Monitoring alarm definitions for CPU, storage utilization, and connection thresholds.
Verify the API key fingerprint you entered matches the one shown in the OCI Console under the user’s API keys, and that the private key was pasted completely and unmodified — including the -----BEGIN PRIVATE KEY----- and -----END PRIVATE KEY----- lines.
Some resources are not showing
Check that the IAM policy is scoped to the correct compartment. If you want to monitor all compartments, use in tenancy rather than in compartment <name> in the policy statements.
Monitoring alarms show as not configured
LowerPlane checks for OCI Monitoring alarm definitions via the Monitoring API. If alarms are managed via Terraform or a third-party tool and don’t appear in the OCI Monitoring service, they won’t be detected. Create alarms in the OCI Console under Monitoring > Alarm Definitions.
Autonomous Database shows public endpoint enabled
ATP databases created with “Secure access from everywhere” have a public endpoint. To fix, edit the database and select “Secure access from specified IPs and VCNs only” or enable private endpoint access.